MCP in Production: Connecting Agents With Least Privilege
In short
What the MCP specification covers for authorisation, what it leaves open, and a permissions matrix for agents in CMS, CRM and ad accounts.
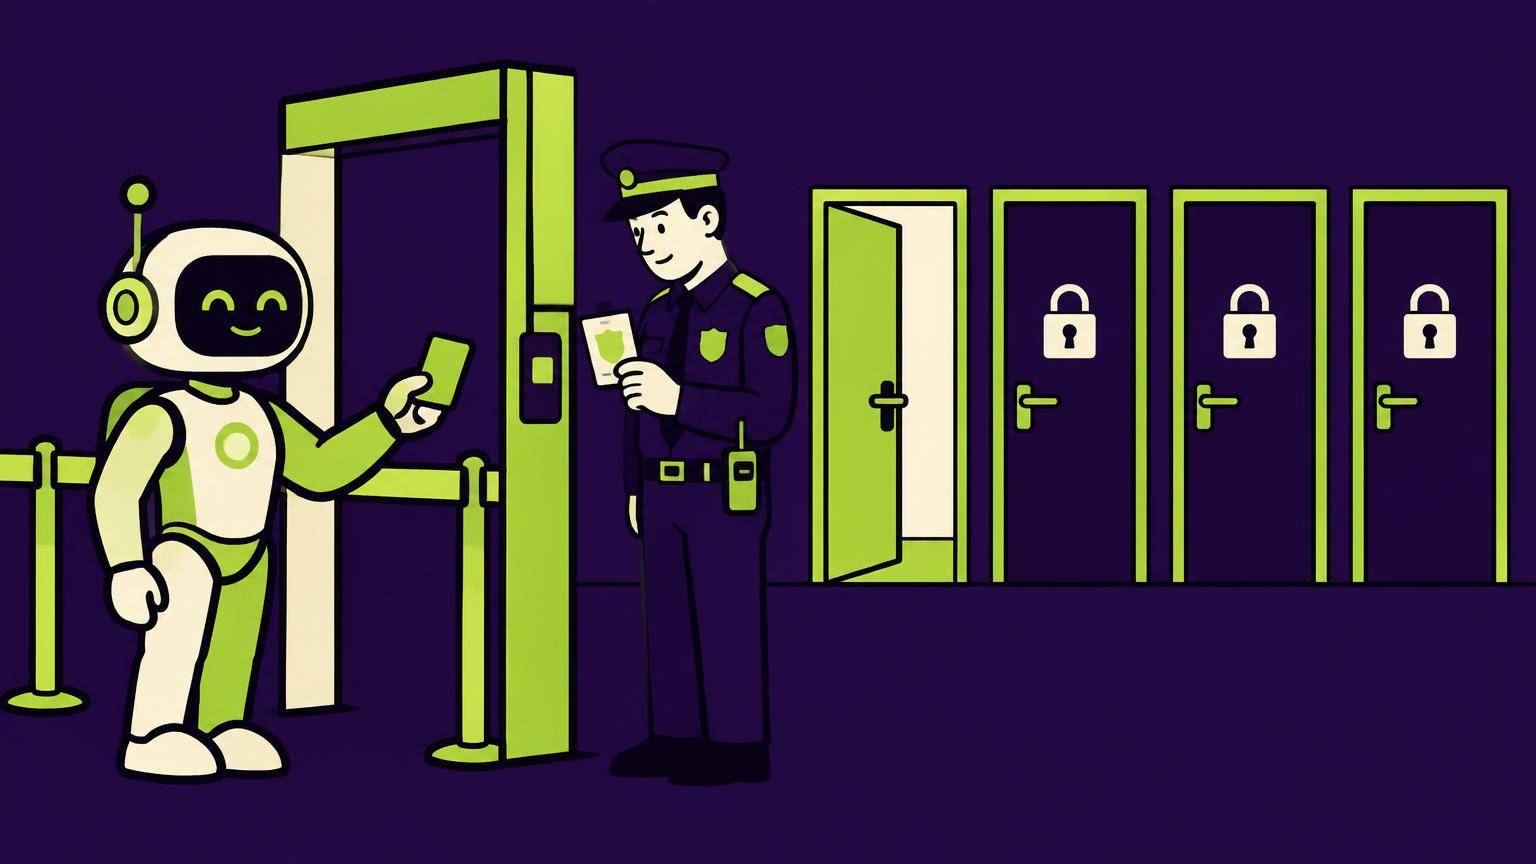
Table of Contents
The Model Context Protocol (MCP) makes it easy to connect an agent to tools. That is exactly the risk: a connection set up in five minutes often grants more rights than the task needs. In production the question is not whether MCP works but what a connected agent is allowed to do.
What the specification covers
The current MCP specification (version 2026-07-28) defines authorisation for HTTP-based transports on top of OAuth 2.1 and related standards such as Protected Resource Metadata and Resource Indicators. Note that authorisation is optional under the specification; for local STDIO connections, credentials should come from the environment instead. The specification therefore governs how a client obtains an access token, not which business actions should be permitted inside the tool.
What stays open, and sits with you
- Scope of rights: whether a token can only read or can also publish is decided by the server or the connected system.
- Agent identity: does the agent act through a person's account or its own machine identity? The latter is usually better for traceability.
- Approvals: which actions need human confirmation?
- Logging: who changed what, when, through which agent?
The OWASP "Top 10 for Agentic Applications 2026" lists exactly these issues, excessive privileges and misuse of tools and identities, among the central risks for agent systems.
Permissions matrix for marketing systems
| System | Read | Create draft | Edit | Publish / budget |
|---|---|---|---|---|
| CMS | Agent | Agent | approval only | Human |
| CRM | Agent (no exports) | Notes | approval only | – |
| Ad account | Reports | Paused drafts | approval only | Human |
| Social planner | Agent | Agent | Agent in draft | Human |
The matrix is a starting point, not a standard. What matters is that each column has a technical counterpart: separate roles, separate tokens or an approval stage inside the system.
Avoid unmanaged connections
When individual employees connect their own MCP servers or browser agents to company accounts, shadow AI appears quickly. A central register of approved servers, an MCP gateway with logging and dedicated non-human identities for agents create visibility without banning every use.
Next step
List the systems agents are already connected to and record the actual rights for each in the matrix. Further reading: agent access without sharing passwords. Check your own position with the agent readiness check.
Sources: MCP specification 2026-07-28: Authorization; OWASP Top 10 for Agentic Applications 2026.
Frequently Asked Questions
What is "MCP in Production: Connecting Agents With Least Privilege" about?
What the MCP specification covers for authorisation, what it leaves open, and a permissions matrix for agents in CMS, CRM and ad accounts.
What the specification covers: what matters?
The current MCP specification (version 2026-07-28) defines authorisation for HTTP-based transports on top of OAuth 2.1 and related standards such as Protected Resource Metadata and Resource Indicators.
What stays open, and sits with you: what matters?
Scope of rights: whether a token can only read or can also publish is decided by the server or the connected system. Agent identity: does the agent act through a person's account or its own machine identity?
Permissions matrix for marketing systems: what matters?
The matrix is a starting point, not a standard. What matters is that each column has a technical counterpart: separate roles, separate tokens or an approval stage inside the system.
Related Articles
You might also be interested in these posts
 Tools & Technology
Agentic RAG: When Company Knowledge Needs More Than Vector Search
Classic RAG, GraphRAG or agentic RAG? A decision grid for brand and product knowledge, with checks for contradictions and sources.
 Tools & Technology
Testing AI Agents: Marketing Workflow Acceptance
A practical acceptance matrix for marketing agents: sources, tool actions, failure cases, approvals and retesting after changes.
 Tools & Technology
AI Agent Frameworks for Marketing 2026: CrewAI, LangGraph & Claude Tasks Compared
The ultimate framework comparison for marketing teams: CrewAI, LangGraph, Claude Tasks and AutoGen in practice – strengths, weaknesses and use cases.